
One portal, one team. Cytek Safeguard™ brings your HIPAA compliance, 24/7 threat monitoring and security reports into one place, built for medical, dental and specialty practices.
Instead of juggling separate tools and vendors, you get one login to see where you stand and one team to call when something happens.
INSIDE SAFEGUARD
Two scores, the factors behind them, and a short list of what to fix next. All in one portal.
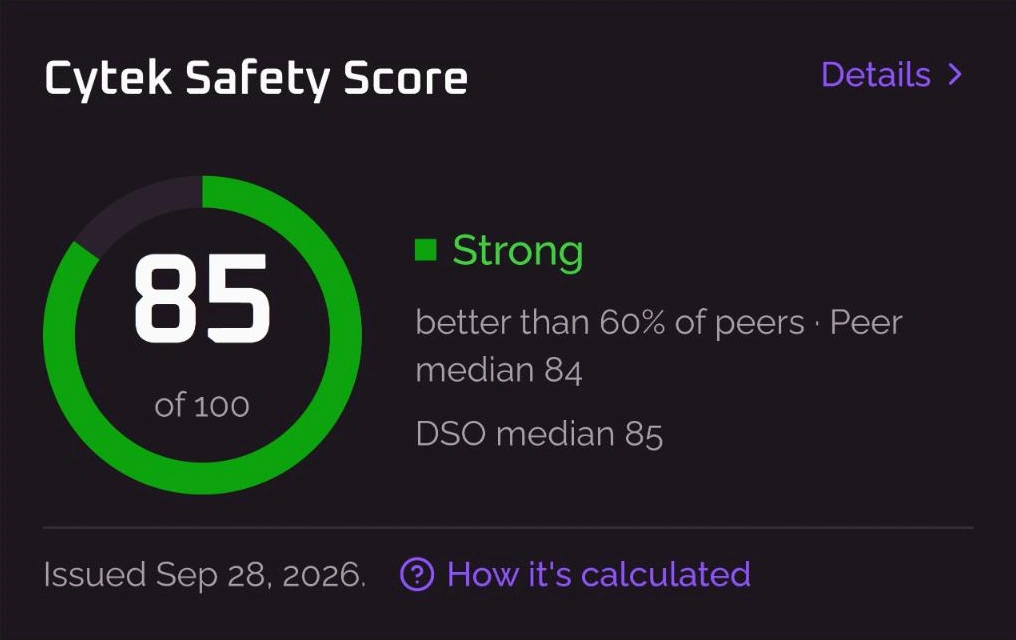
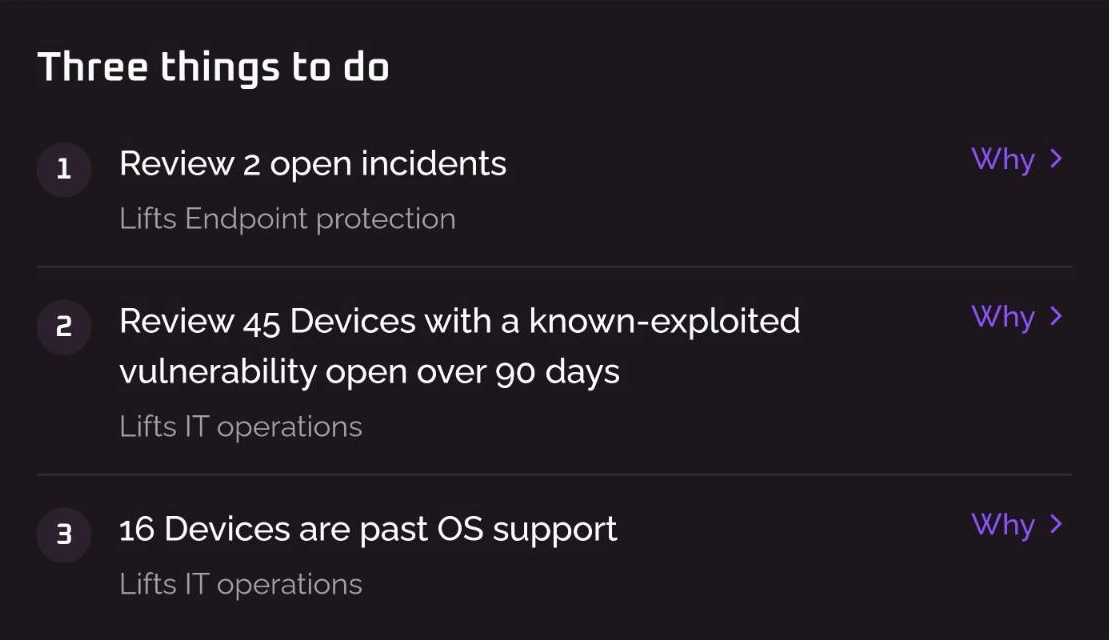
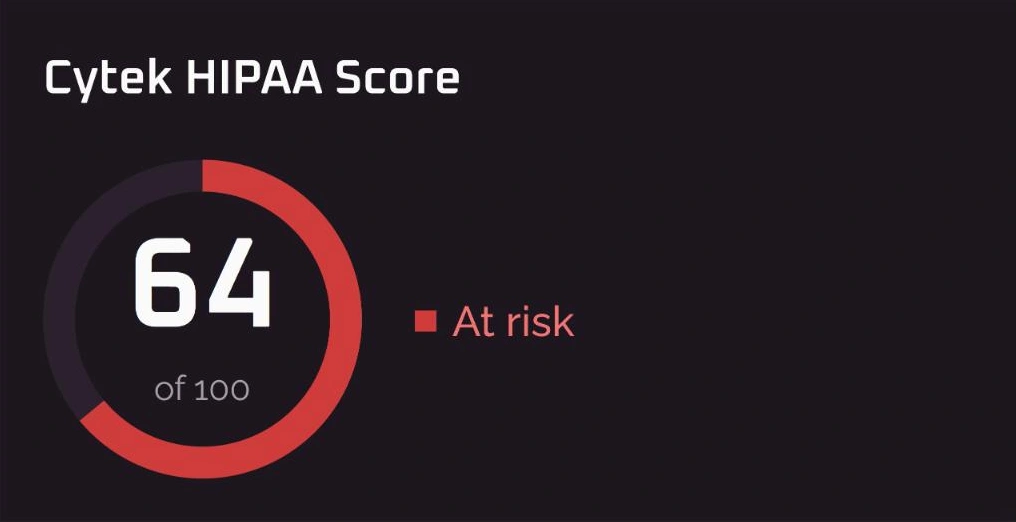
Demo data from the Safeguard portal
01
Most practices end up with a patchwork: antivirus from one vendor, email security from another, a compliance binder on a shelf and nobody watching the logs at night. Safeguard pulls it together.
When something needs attention, you hear from our analysts, not a ticket queue.
02
| Module | HIPAA Security Rule |
|---|---|
| 24/7 MDR | Security incident procedures, 164.308(a)(6); protection from malicious software, 164.308(a)(5)(ii)(B) |
| SIEM | Audit controls, 164.312(b); information system activity review, 164.308(a)(1)(ii)(D); log-in monitoring, 164.308(a)(5)(ii)(C) |
| ITDR | Person or entity authentication, 164.312(d); log-in monitoring |
| Vulnerability scanning | Risk analysis and risk management, 164.308(a)(1)(ii)(A) and (B); evaluation, 164.308(a)(8) |
| Asset inventory | Risk analysis; device and media accountability, 164.310(d)(2)(iii) |
| Security score | Risk management; evaluation, 164.308(a)(8) |
HHS has also proposed an update to the Security Rule that would require a written technology asset inventory and network map, vulnerability scans at least every six months, a penetration test every year and multi-factor authentication. As of November 2026 it is still a proposal, and Safeguard already covers those items.
03
You shouldn't need a security team to understand your security. Safeguard reports are written in plain language, ranked by what matters most and tied to what HIPAA expects. Your office manager can see the status at a glance, and your IT provider gets the technical detail needed to fix things.
Already working with an IT company? Safeguard works alongside them. If you need one, our sister company Xceltek supports healthcare practices nationwide.
Modules
Start with what you need now and add more as you grow.
24/7 MDR
Round-the-clock threat detection and response for every computer and server.
Learn more →SIEM and log monitoring
Collect and review activity logs to catch threats and meet HIPAA audit controls.
Learn more →ITDR for Microsoft 365
Spot stolen logins, risky sign-ins and email forwarding rules, then shut them down.
Learn more →Vulnerability scanning
Regular scans with plain-language reports ranked by risk.
Learn more →Asset inventory
A live list of every device that touches patient data.
Learn more →Security score
One number that shows where you stand and what to fix next.
Learn more →HIPAA compliance tools
Risk assessments, policies, training and documentation in one place.
Learn more →Secure Mail
Encrypted email for patient information that staff actually use.
Learn more →Phishing training
Simulated phishing and short training that changes behavior.
Learn more →FAQ
Safeguard is a security and HIPAA compliance platform for healthcare practices. It combines 24/7 MDR, SIEM, ITDR, vulnerability scanning, asset inventory and a security score with HIPAA risk assessments, policies and training, all in one portal.
No. Many practices start with a risk assessment and the compliance tools, then add monitoring. We will recommend what fits your size and risk.
Our analysts. Threats are monitored around the clock, and our team contacts you directly with what happened and what was done about it.
No. It works alongside your IT provider. We handle security monitoring and compliance and share findings with whoever manages your systems.
It depends on your number of users, devices and locations and which modules you choose. Talk to an analyst for a quote.
Sources: 45 CFR 164.308, administrative safeguards · 45 CFR 164.310, physical safeguards · 45 CFR 164.312, technical safeguards · HHS fact sheet on the proposed Security Rule update. This page is general information, not legal advice.
Take the free risk assessment, or talk to an analyst about which modules fit.
